
Koniag Government Services has achieved Cybersecurity Maturity Model Certification Level 2 through an independent assessment conducted by an authorized Certified Third-Party Assessment Organization.
CMMC Level 2 is the Defense Department’s mandatory cybersecurity standard for contractors handling Controlled Unclassified Information. The certification validates KGS has implemented all 110 security requirements outlined in NIST SP 800-171, verified through third-party assessment.
“Our defense mission partners entrust us with critical programs and sensitive information that directly impact national security,” said Matt Carle, chief operating officer, Defense Line of Business at KGS. “CMMC Level 2 certification validates that we have the robust cybersecurity controls and discipline required to honor that trust. This milestone ensures we can continue to securely support our customers in the DoW’s increasingly complex mission.”
As of January 2025, fewer than 800 organizations across the Defense Industrial Base have achieved CMMC Level 2 certification, less than 1% of the roughly 118,000 companies expected to require it. The CMMC program became mandatory under a final rule published in October 2024, requiring defense contractors to undergo independent third-party assessments to verify cybersecurity practices.
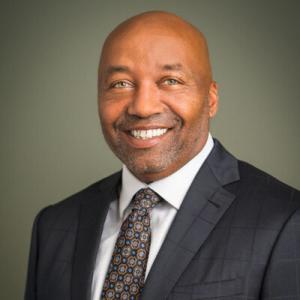
“Achieving CMMC Level 2 certification demonstrates our unwavering commitment to protecting sensitive government information and supporting our mission partners with the highest levels of cybersecurity assurance,” said Kevin Wideman, CEO at KGS. “This milestone strengthens our competitive position and reduces program delivery risk as cybersecurity requirements become increasingly critical across the federal contracting landscape.”
The company will maintain its certification through continuous monitoring, disciplined change control processes, and ongoing evidence readiness to ensure sustained compliance with evolving cybersecurity requirements.